Under Articles 24–25, financial entities other than micro-enterprises must run a risk-based testing programme and, at least annually, test the systems supporting their critical or important functions. DORA lists appropriate methods (such as vulnerability assessments, network assessments, scenario-based and penetration testing) — not every method is mandatory for every entity.
This is the testing tier that applies to most Irish firms. It is also the one most often misdescribed, so it is worth being precise about what DORA actually requires.
The testing programme (Article 24)
Non-micro entities must establish and maintain a proportionate, risk-based digital operational resilience testing programme as part of their ICT risk management. It is not a one-off: it is an ongoing, documented programme reviewed over time.
What must be tested, and how often
At least annually, appropriate tests must be conducted on all ICT systems and applications supporting critical or important functions. The methods are chosen by risk — DORA lists options rather than mandating all of them:
Vulnerability assessments and scans
Network security assessments
Gap analyses and physical-security reviews
Scenario-based and end-to-end testing
Penetration testing
Tests may be carried out by independent internal or external parties. Micro-enterprises are not exempt — they test using a proportionate, risk-based approach.
How this differs from TLPT
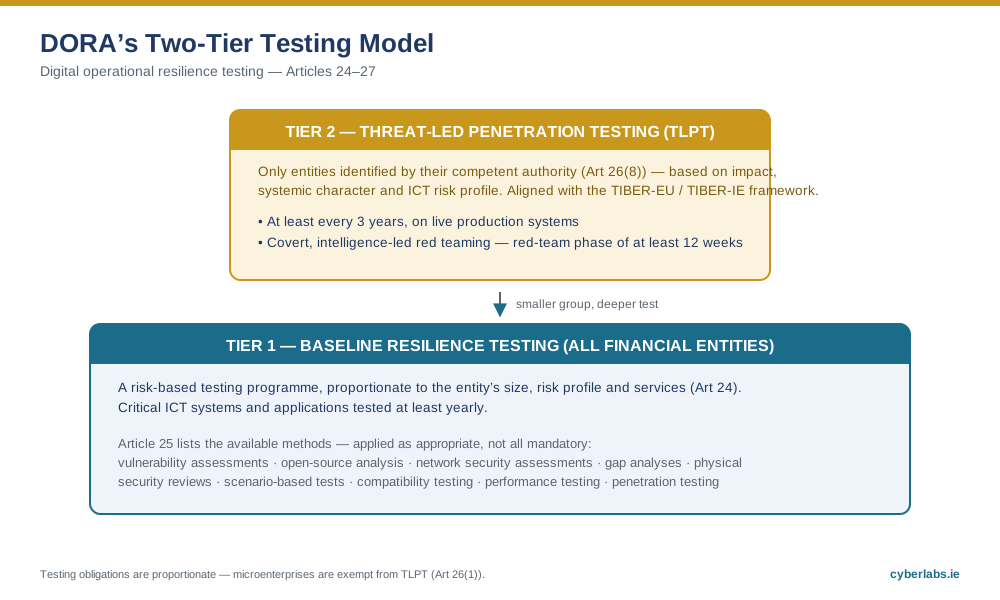
Baseline testing is the wide-net obligation. TLPT (Articles 26–27) is the advanced, intelligence-led exercise required only for entities identified by their competent authority. Most firms do baseline testing only. See Pentest vs TLPT.
Frequently asked questions
Does every DORA entity need penetration testing?
No. DORA requires appropriate ICT testing, but does not require every entity to run a penetration test in every cycle. Article 25 lists penetration testing as one of several methods. Non-micro entities must ensure appropriate testing at least annually on systems supporting critical or important functions; micro-enterprises follow a proportionate, risk-based approach.
Want a testing programme scoped to your actual obligation? See our DORA testing services.